Again this year was ShmooCon's Ghost in the Shellcode warm-up round or Teaser (@ShellGhostCode). Congrats to Eindbazen for winning!
There was three challenges: crypto (Tel Aviv), crackme (AL's revenge) and exploitation (Hackquest). You will notice strong references to Hackers (1995) movie. Write-ups can be found on FixMe wiki, Leet More blog or Eindbazen blog.
Showing posts with label cop. Show all posts
Showing posts with label cop. Show all posts
Sunday, January 08, 2012

Friday, April 29, 2011
pCTF 2011 #18 A small bug
Challenge #18 "A small bug" was a common TOCCTOU bug very interesting to exploit reliably.
@hellman already did a write-up on this challenge. His exploit reads the file name on stderr and hopes to win the race on symlink creation. But actually there is a way to win the race every time! Let's see that.
@hellman already did a write-up on this challenge. His exploit reads the file name on stderr and hopes to win the race on symlink creation. But actually there is a way to win the race every time! Let's see that.
Wednesday, April 27, 2011
pCTF 2011 #19 Another small bug
Challenge #19 "Another small bug" was a stack-based buffer overflow.
Djo (@shell_storm) has already published a write-up (english) on Nibbles' blog, as well as @hellman on Leet More's blog, and Agix (@Agixid) on shell-storm. Just like hashcalc1 or hashcalc2, there was no NX. However, ASLR was enabled. Djo and hellman both used a big nopsled + brute-force to circumvent ASLR, Agix used a nice ret2ret, while I chose ROP to mmap rwx. Good thing is that it would also have worked if NX had been effectively enabled.
Not familiar with ROP? Have a look at the references posted on this exploit writing tutorial by @corelanc0d3r.
Djo (@shell_storm) has already published a write-up (english) on Nibbles' blog, as well as @hellman on Leet More's blog, and Agix (@Agixid) on shell-storm. Just like hashcalc1 or hashcalc2, there was no NX. However, ASLR was enabled. Djo and hellman both used a big nopsled + brute-force to circumvent ASLR, Agix used a nice ret2ret, while I chose ROP to mmap rwx. Good thing is that it would also have worked if NX had been effectively enabled.
Not familiar with ROP? Have a look at the references posted on this exploit writing tutorial by @corelanc0d3r.
Tuesday, April 26, 2011
pCTF 2011 #26 Hashcalc2
pCTF 2011 #22 Hashcalc1
Challenge #22 "Hashcalc 1" was binary exploitation over the network.
A good write-up is already available on sleepya's blog. He made an exploit bypassing any ASLR/NX using ROP.
However, NX was not enabled on the wargame machine... Organizers thought they did, but it was not effective :( Good for us it means only ASLR, and the binary was not even PIE. One could exploit it quickly by writing a shellcode in the GOT, let's see that.
A good write-up is already available on sleepya's blog. He made an exploit bypassing any ASLR/NX using ROP.
However, NX was not enabled on the wargame machine... Organizers thought they did, but it was not effective :( Good for us it means only ASLR, and the binary was not even PIE. One could exploit it quickly by writing a shellcode in the GOT, let's see that.
pCTF 2011 #32 That's no bluetooth
The only networking problem at pCTF 2011 was unusual because it involved ZigBee, based on IEEE 802.15.4.
Context
We captured this network traffic from outside of an AED employee's home.

Decrypt it and find the key.

Update: Our operatives were able to decrypt packet #18 in the capture file.

The decrypted data is 18060a0700421a63343a636f6e74726f6c345f73723235303a43342
d53523235300400420830332e30312e3534050020040600213c00
or (printable text only) Bc4:control4_sr250:C4-SR250B03.01.54 !<

If you aren't getting the correct values, make sure your keys are correct,
and that they are entered correctly. Keep in mind bits sometimes flip when
transmitting signals wirelessly.
download file
Monday, April 25, 2011
Plaid Parliament of Pwning CTF 2011
As @dinodaizovi nicely put on twitter, CTF team Plaid Parliament of Pwning have gone from winning everyone else's CTFs to hosting their own, namely the plaid CTF or pCTF (@pctf2011). It was 48 hours of intense challenge-based CTF like Defcon quals.
I expected a lot of fun challenges for this CTF because PPPs are highly skilled in areas such as binary exploitation. And I wasn't disappointed! Expect a few write-ups from me in the following posts :)
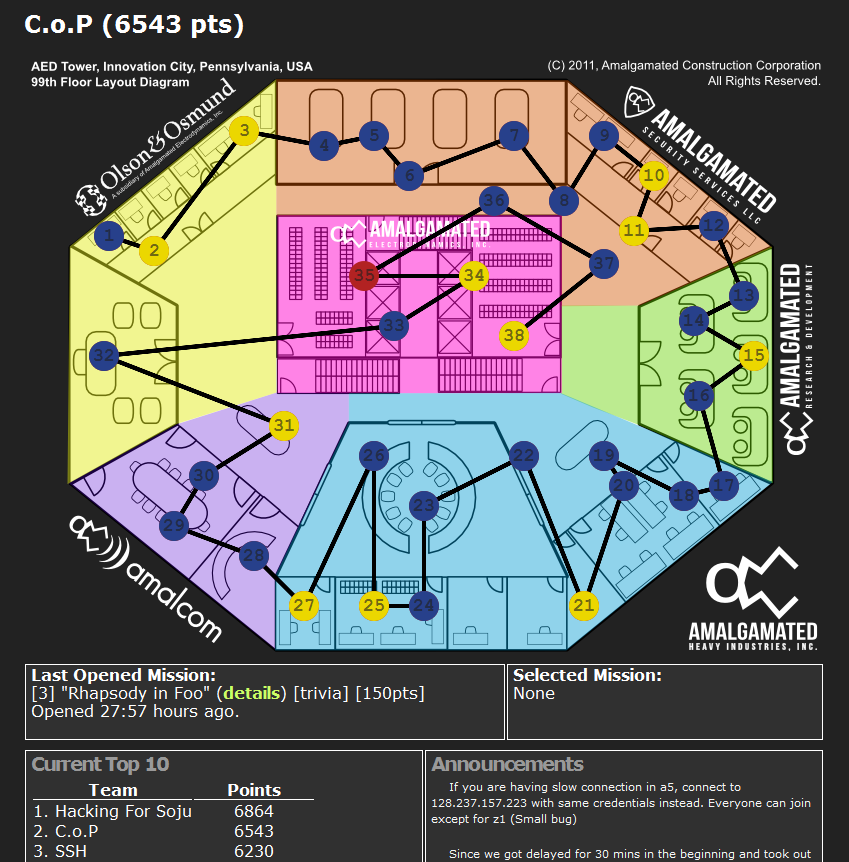
As you can see on the final scoreboard, more than 400 teams registered and 155 teams scored points. Since I no longer play with Nibbles guys, this time I played with a new team called CoP. We got the 2nd place, 1st place being taken at the last moment by our CTF friends HFS (Hacking for Soju). Good game, it was intense!

Congratulations to everyone for playing, and especially to PPP members who made this CTF possible. Very good challenges, organization, and IRC presence for support. You pwn guys!
If you want to have a look at the challenges, I mirrored them here (except remote/web of course), along with screenshots of problems, scoreboard, etc.
I expected a lot of fun challenges for this CTF because PPPs are highly skilled in areas such as binary exploitation. And I wasn't disappointed! Expect a few write-ups from me in the following posts :)
As you can see on the final scoreboard, more than 400 teams registered and 155 teams scored points. Since I no longer play with Nibbles guys, this time I played with a new team called CoP. We got the 2nd place, 1st place being taken at the last moment by our CTF friends HFS (Hacking for Soju). Good game, it was intense!

Congratulations to everyone for playing, and especially to PPP members who made this CTF possible. Very good challenges, organization, and IRC presence for support. You pwn guys!
If you want to have a look at the challenges, I mirrored them here (except remote/web of course), along with screenshots of problems, scoreboard, etc.
Subscribe to:
Posts (Atom)